Project overview
Our client needed to streamline and automate the CI/CD pipeline for their Java application running on Kubernetes, ensuring both code quality and security compliance across the development and deployment lifecycle. They wanted a solution that could accelerate delivery while reducing manual effort.
Challenges
- Manual code reviews and security scans: Code quality and security vulnerabilities were inconsistently addressed, leading to delays and increased risk.
- Continuous integration and delivery: Manual builds and deployments increased the likelihood of human error.
- Security compliance: Robust, automated security checks for Docker images and Kubernetes deployment files were needed to maintain compliance.
Proposed solution & architecture
Unified Techs designed and implemented a fully automated CI/CD pipeline using AWS native services, focusing on both code quality and security. The solution ensured that every step — from code commits to Kubernetes deployments — was automated, secure and consistent. The pipeline included the following key stages:
Pipeline stages
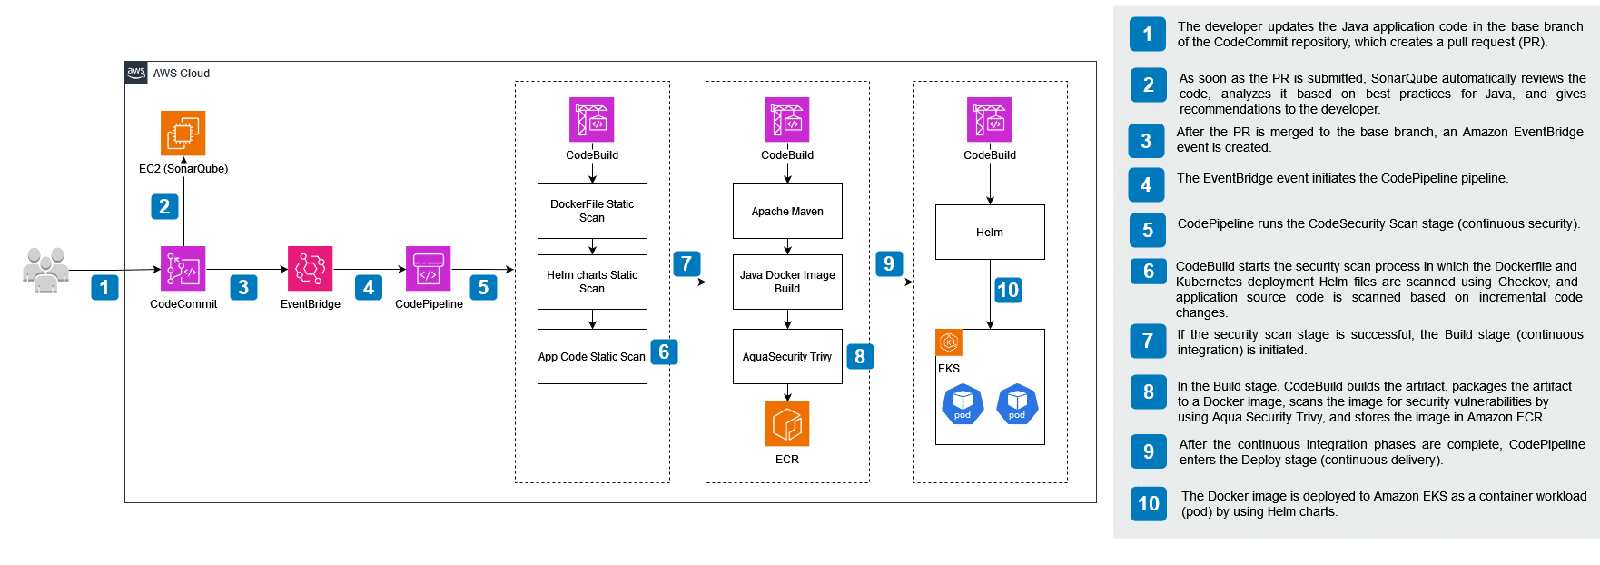
- Code review automation with SonarQube: When a developer submits a pull request in the CodeCommit repository, SonarQube automatically analyzes the Java code for best practices and provides direct feedback.
- Event-driven pipeline triggering: After a pull request merge, Amazon EventBridge triggers the CI/CD pipeline automatically, eliminating the need for manual starts.
- Continuous security scanning: CodeBuild scans the Dockerfile and Kubernetes Helm deployment files using Checkov. Aqua Security Trivy scans the resulting Docker image for vulnerabilities before pushing it to Amazon Elastic Container Registry.
- Continuous integration and build: CodeBuild packages the artifact into a Docker image and verifies that it meets security standards before allowing it to proceed to deployment.
- Continuous delivery to Kubernetes: The Docker image is automatically deployed to Amazon EKS using Helm charts, ensuring consistent, repeatable and secure deployments.
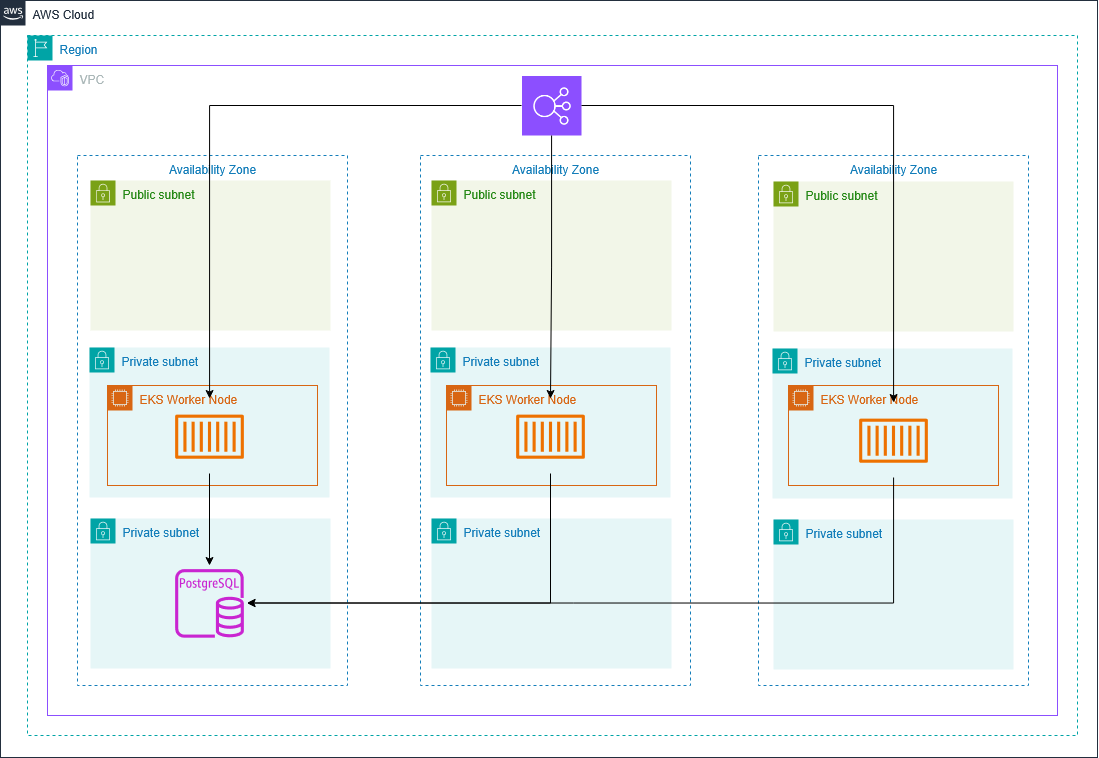
Architecture
Metrics for success
- Improved code quality: Automated analysis reduced manual review time and improved adherence to standards.
- Enhanced security: Vulnerabilities were identified early, lowering the risk of production issues.
- Faster time to production: Deployment times were reduced by 50% through automation.
- Increased developer efficiency: Developers could focus on coding while the pipeline handled testing, security scanning and Kubernetes deployments.
Lessons learned
- Automation enhances security: Continuous scanning integrated into the pipeline improved compliance and reduced vulnerabilities.
- Efficiency through integration: Automating the CI/CD process from code commits to Kubernetes deployments boosted both speed and reliability.
Technologies used
FAQ
What AWS services were used in this engagement?
AWS CodeCommit, Amazon EventBridge, AWS CodeBuild, Amazon ECR and Amazon EKS, with SonarQube, Checkov and Aqua Security Trivy gating every merge.
What were the measurable outcomes?
Deployment times were reduced by 50%, vulnerabilities were caught before production, and developers could focus on coding while the pipeline handled testing, scanning and deployment.